Tutte le segnalazioni del canale Telegram OsintOps News dal 2025 a oggi: strumenti, articoli e risorse OSINT scelti dalla redazione. Ogni notizia rimanda alla fonte originale.
82 notizie
- github.com
CHRONOS
GO tool to download and analyze archive org snapshots: – search regex matches – extract endpoints from JS fils – calculate old favicon…
Leggi tutto
GO tool to download and analyze archive org snapshots: – search regex matches – extract endpoints from JS fils – calculate old favicon hashes – extract html tags with XPath https://github.com/mhmdiaa/chronos from cybdetective
- airisk.mit.edu
What are the risks from Artificial Intelligence?A comprehensive living database of over 1000 AI risks categorized by…
What is the AI Risk Repository? The AI Risk Repository has three parts: 1) The AI Risk Database captures 1000+ risks extracted from 56…
Leggi tutto
What is the AI Risk Repository? The AI Risk Repository has three parts: 1) The AI Risk Database captures 1000+ risks extracted from 56 existing frameworks and classifications of AI risks 2) The Causal Taxonomy of AI Risks classifies how, when, and why these risks occur 3) The Domain Taxonomy of AI Risks classifies these risks into 7 domains (e.g., “Misinformation”) and 23 subdomains (e.g., “False or misleading information”)
- darkreading.com
SANS Institute Launches AI Cybersecurity Hackathon
As AI adoption accelerates, organizations lack the tools to secure these rapidly evolving technologies. While AI's potential in…
Leggi tutto
As AI adoption accelerates, organizations lack the tools to secure these rapidly evolving technologies. While AI's potential in cybersecurity is vast, there is currently a significant gap between innovation and implementation. Many existing security solutions are either proprietary, insufficient, or simply inaccessible. SANS Institute, the global leader in cybersecurity training and research, is launching the AI Cybersecurity Hackathon, a month-long event designed to address the urgent need for the development of these tools. The hackathon aims to inspire participants to develop expertise in AI security, identify and support cybersecurity talent, and drive progress in AI security research through open-source contributions. Running from February 15 to March 15, 2025, this hackathon provides an opportunity for cybersecurity professionals, ethical hackers, developers, and students to cultivate the critical skills and develop the open-source tools needed to address emerging AI security challenges.
- github.com
https://github.com/JackJuly/linkook
- cloud.google.com
Adversarial Misuse of Generative AI
This report shares our findings on government-backed threat actor use of the Gemini web application. The report encompasses new findings…
Leggi tutto
This report shares our findings on government-backed threat actor use of the Gemini web application. The report encompasses new findings across advanced persistent threat (APT) and coordinated information operations (IO) actors tracked by GTIG. By using a mix of analyst review and LLM-assisted analysis, we investigated prompts by APT and IO threat actors who attempted to misuse Gemini. Our key findings include: – We did not observe any original or persistent attempts by threat actors to use prompt attacks or other machine learning (ML)-focused threats as outlined in the Secure AI Framework (SAIF) risk taxonomy. Rather than engineering tailored prompts, threat actors used more basic measures or publicly available jailbreak prompts in unsuccessful attempts to bypass Gemini's safety controls. – Threat actors are experimenting with Gemini to enable their operations, finding productivity gains but not yet developing novel capabilities. At present, they primarily use AI for research, troubleshooting code, and creating and localizing content. – APT actors used Gemini to support several phases of the attack lifecycle, including researching potential infrastructure and free hosting providers, reconnaissance on target organizations, research into vulnerabilities, payload development, and assistance with malicious scripting and evasion techniques. Iranian APT actors were the heaviest users of Gemini, using it for a wide range of purposes. Of note, we observed limited use of Gemini by Russian APT actors during the period of analysis. – IO actors used Gemini for research; content generation including developing personas and messaging; translation and localization; and to find ways to increase their reach. Again, Iranian IO actors were the heaviest users of Gemini, accounting for three quarters of all use by IO actors. We also observed Chinese and Russian IO actors using Gemini primarily for general research and content creation. – Gemini's safety and security measures restricted content that would enhance adversary capabilities as observed in this dataset. Gemini provided assistance with common tasks like creating content, summarizing, explaining complex concepts, and even simple coding tasks. Assisting with more elaborate or explicitly malicious tasks generated safety responses from Gemini. – Threat actors attempted unsuccessfully to use Gemini to enable abuse of Google products, including researching techniques for Gmail phishing, stealing data, coding a Chrome infostealer, and bypassing Google's account verification methods.
- sashaingber.substack.com
The 23-year-old who infiltrated a North Korean laptop farm
Aidan Raney documented an operation to exploit U.S. businesses, one of the ways North Korea funds its weapons of mass destruction and…
Leggi tutto
Aidan Raney documented an operation to exploit U.S. businesses, one of the ways North Korea funds its weapons of mass destruction and ballistic missile programs.
- maigret.readthedocs.io
🎉 Maigret finally has a web interface mode!
What feature should we implement next? 👇🤔 A huge shoutout to the amazing community for supporting Maigret's development, suggesting…
Leggi tutto
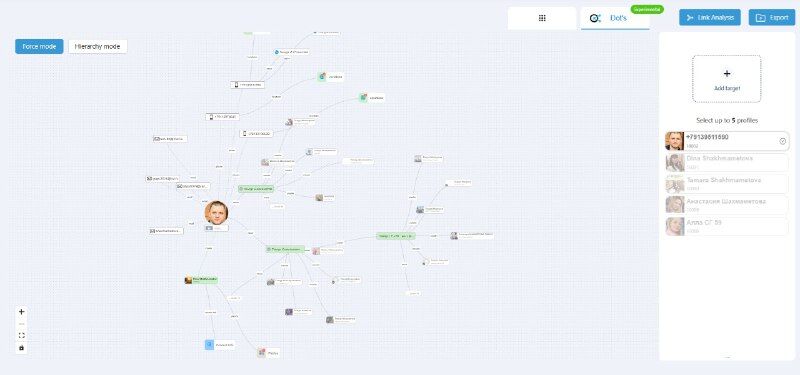
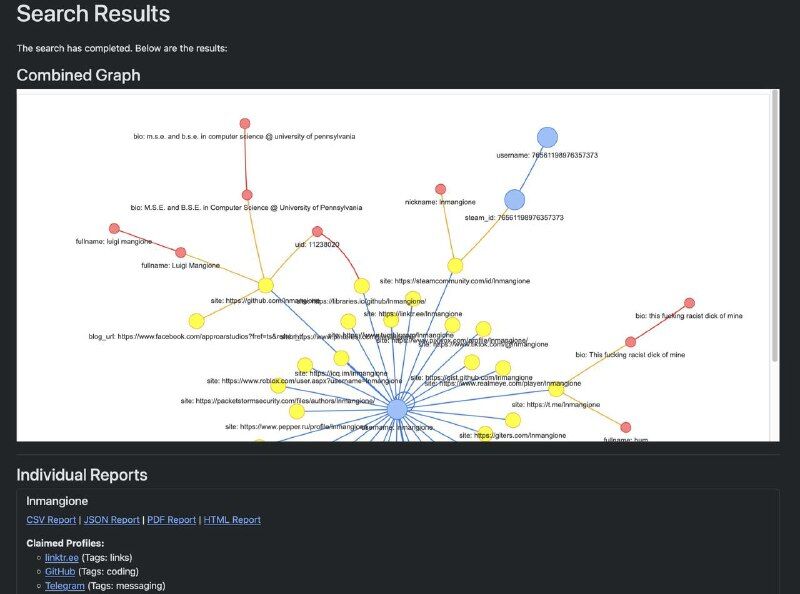
What feature should we implement next? 👇🤔 A huge shoutout to the amazing community for supporting Maigret's development, suggesting improvements, and even adding new features. 🙌 👉 Instructions on Read the Docs Special thanks to overcuriousity for creating the web interface! ❤️ — In my opinion, there aren't many developers in the industry willing to dedicate their time and effort to improving open-source OSINT tools. Massive respect for all of you – your work is invaluable! 💪✨ P.S. The screenshot shows a graph of data from Luigi Mangione’s accounts – check out this post with a full investigation graph. #maigret #github #investigation