Tutte le segnalazioni del canale Telegram OsintOps News dal 2025 a oggi: strumenti, articoli e risorse OSINT scelti dalla redazione. Ogni notizia rimanda alla fonte originale.
82 notizie
- medium.com
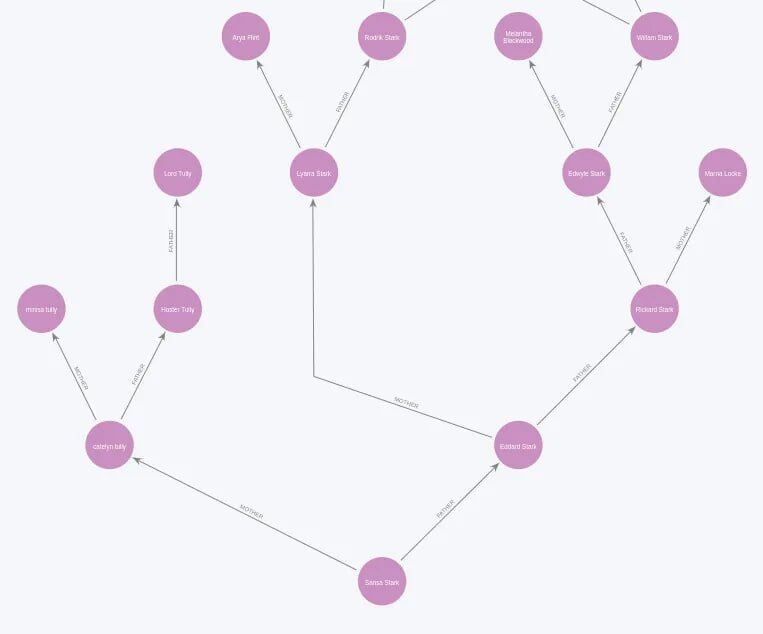
Investigate family connections between House of the Dragon and Game of Thrones characters
This blog post will teach you how to interactively search and visualize relationships between various characters that require no coding or…
Leggi tutto
This blog post will teach you how to interactively search and visualize relationships between various characters that require no coding or Cypher knowledge. If you are a data analyst or aspire to become one, I will show you how to execute graph algorithms from a Python Notebook and evaluate their results in the last part of this blog.
- Telegram
Terrorist Misuse of AI: A Framework for U.S.-PRC Cooperation
Both the United States and China recognize the need to prevent non-state actors, particularly terrorist organizations, from exploiting AI…
Leggi tutto
Both the United States and China recognize the need to prevent non-state actors, particularly terrorist organizations, from exploiting AI for malicious purposes, including CBRN-related threats. The rapid development and growing accessibility of advanced AI models increase these risks, highlighting the need for coordinated technical and operational safeguards. A focused bilateral framework is therefore proposed to counter terrorist misuse of AI, independent of broader geopolitical tensions and in the interest of international security.
- youtube.com
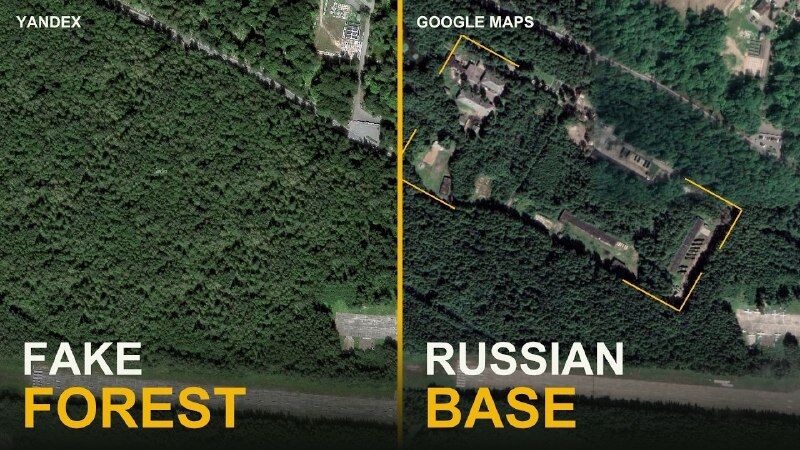
The Russian Base Hidden Beneath a Fake Forest on Satellite Maps
A Russian military base appears as a forest on Yandex satellite imagery. So how can you check what is really there, and whether the image…
Leggi tutto
A Russian military base appears as a forest on Yandex satellite imagery. So how can you check what is really there, and whether the image you’re looking at is accurate? In this OSINT tutorial, I investigate a fake forest in Russia near St Petersburg, compare it with Google Earth and Esri World Imagery Wayback, and examine another example in central Seoul, South Korea. The site in Russia was first identified by Finnish broadcaster Yle, and in this session I show how repeated patterns, inconsistent edges and comparisons with other imagery can reveal what a public satellite map has obscured. This is also a practical tutorial on how to verify satellite images you come across in news reports, on social media or in your own research. We work through how to identify what an image shows, confirm its location, check when it was captured, and assess whether it supports the claims being made about it. YOU’LL LEARN HOW TO • Spot repeated textures and other signs of image manipulation. • Match locations using roads, buildings, runways and natural features. • Compare the same site across different map services. • Use historical imagery to check changes over time. • Distinguish an image’s capture date from its publication date. • Apply a simple verification checklist: source, location, date and comparison. Different imagery does not automatically mean manipulation. Capture dates, resolution, seasons and real changes on the ground can all affect what you see. The aim is to cross-check the evidence and understand what an image can, and cannot, tell you.
- youtube.com
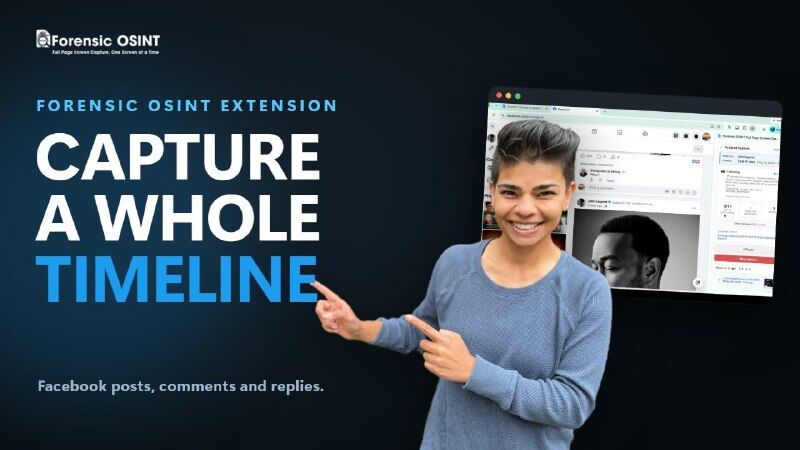
Facebook Timeline Capture: Preserve a Whole Date Range of Posts and Comments
Facebook Timeline Capture in the Forensic OSINT extension. You set a date range, and the extension opens every post inside it, switches each…
Leggi tutto
Facebook Timeline Capture in the Forensic OSINT extension. You set a date range, and the extension opens every post inside it, switches each one to All comments, expands the replies, and captures it screen by screen. Ritu Gill runs a real capture end to end, from detection-risk check to the finished PDF report. What you'll learn: ✅ See what a Facebook timeline run does before you start one ✅ Open Assisted Capture from a Facebook profile ✅ Check detection risk and account practices before a run ✅ Pick a date range and know what discovery will read ✅ Run discovery and read the live log while it works ✅ Review the in-range posts and approve what gets captured ✅ Know what to expect while a run works through the list ✅ Review captures in Case Management and export the report
- github.com
OSInt Graph
Visual exploration of OSINT data for investigative cases: people, phones, e-mails, social profiles, vehicles, places and documents as an…
Leggi tutto
Visual exploration of OSINT data for investigative cases: people, phones, e-mails, social profiles, vehicles, places and documents as an interactive graph, with everything stored locally on your computer.
- anubitux.org
New AnuBitux version 3.5.6 is out! https://anubitux.org/download-anubitux/
– Tools updated – BlindMnemonic improved – Obsolete tools removed
- osintops.com
OSInt on China: a look beyond the great wall
This is the opening chapter of Wukong, the new OsintOps project: articles and a dedicated VM to learn how to search beyond the Great…
Leggi tutto
This is the opening chapter of Wukong, the new OsintOps project: articles and a dedicated VM to learn how to search beyond the Great Firewall.
- osintops.com
Exploratores
Repo Exploratores is out: my OSINT toolbox, almost nine hundred search options running from a HTML tool, with a local copy of CyberChef and…
Leggi tutto
Repo Exploratores is out: my OSINT toolbox, almost nine hundred search options running from a HTML tool, with a local copy of CyberChef and Redactor. No central server, no tracking: what happens in your browser stays in your browser.
- osintops.com
AI Can Multiply Expertise, Not Replace It
- osintops.com
Why we built the Multilingual OSINT Glossary?
When you work in a multicultural environment, sooner or later you’ll find yourself looking up the exact meaning of a term you might need to…
Leggi tutto
When you work in a multicultural environment, sooner or later you’ll find yourself looking up the exact meaning of a term you might need to study a text, prepare a presentation, or talk with other OSINT experts who don’t speak your language… and so on. So we decided to start work on a Multilingual OSINT Glossary. It collects over 130 entries from five different but authoritative sources: the Berkeley Protocol for digital investigations soxoj’s Counter-OSINT Guide for countermeasures and digital hygiene the Team Cymru, SANS and NICCS glossaries for threat intelligence and cybersecurity We put quite a bit of work into building it and gathering terms in four different languages (English, Russian, simplified Chinese/pinyin and Italian).
- osint-ui.com
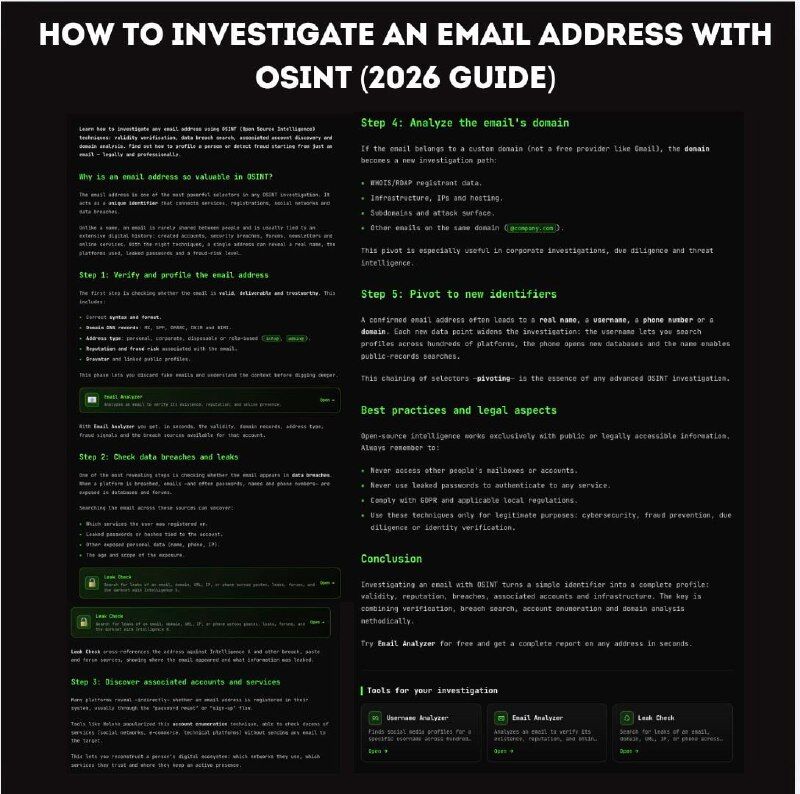
How to Investigate an Email Address with OSINT (2026 Guide)
Learn how to investigate any email address using OSINT (Open Source Intelligence) techniques: validity verification, data breach search…
Leggi tutto
Learn how to investigate any email address using OSINT (Open Source Intelligence) techniques: validity verification, data breach search, associated account discovery and domain analysis. Find out how to profile a person or detect fraud starting from just an email — legally and professionally.
- osintops.com
We’ve refreshed OsintOps.com!
A blog about OSINT that doesn’t get updated already has one foot in the grave. That’s why over the past few weeks we decided to come back to…
Leggi tutto
A blog about OSINT that doesn’t get updated already has one foot in the grave. That’s why over the past few weeks we decided to come back to osintops.com and get it moving again. Nothing revolutionary — the nature of the blog stays the same. What changes is the frame, plus a couple of new sections that simply didn’t exist until yesterday.
- osintops.com
Argos is back, and it’s not flying solo
While the osintops blog is being slowly brought back online, we kept working on two projects that have proven useful for our day-to-day work…
Leggi tutto
While the osintops blog is being slowly brought back online, we kept working on two projects that have proven useful for our day-to-day work and in which we are investing a fair amount of time. We have given Argos a new lease of life and, building on the experience gained, we have developed the first beta of Speculator.
- visualnotes.tech
Operation Viper-Ghost
Brand Impersonation × Suspicious Remote Hire Investigationlink This is a fictional training exercise created for educational purposes as…
Leggi tutto
Brand Impersonation × Suspicious Remote Hire Investigationlink This is a fictional training exercise created for educational purposes as part of the VisualNotes OSINT Training Series. All persons, companies, domains, IP addresses, and events described in this case file are entirely simulated and do not represent real individuals or entities. The techniques described are documented for defensive security awareness and analyst training only. Readers should not apply any OSINT methodology against real individuals without proper legal authorization. Unauthorized investigation of real persons may violate privacy laws including GDPR, IT Act 2000, and equivalent legislation in your jurisdiction. Part of the VisualNotes OSINT Training Series TLP:AMBER · For training use only · visualnotes.tech
- github.com
Awesome OSINT MCP
By @soxoj https://github.com/soxoj/awesome-osint-mcp-servers A curated list of MCP servers for OSINT (Open Source Intelligence). An MCP…
Leggi tutto
By @soxoj https://github.com/soxoj/awesome-osint-mcp-servers A curated list of MCP servers for OSINT (Open Source Intelligence). An MCP server connects tools and services to LLM systems like Claude, Cursor, Windsurf, etc. MCP servers simplify execution of OSINT tools by combining them with the ease of LLM querying and the ability to create flexible reports.
- github.com
WIRETAPPER
WireTapper monitors wireless signals to map surroundings without broadcasting data. This open source tool detects Wi-Fi networks, Bluetooth…
Leggi tutto
WireTapper monitors wireless signals to map surroundings without broadcasting data. This open source tool detects Wi-Fi networks, Bluetooth devices, cell towers, and IoT hardware in real time. You link the software with databases like WiGle or OpenCellID to locate hidden infrastructure and identify security vulnerabilities. Analysts use this passive approach for stealthy reconnaissance. This method leaves no digital footprint on target networks. WireTapper provides immediate situational awareness for your signal intelligence operations. High quality hardware improves results because signal detection range depends on antenna sensitivity and environmental interference. Check local regulations before monitoring signals to ensure compliance with regional privacy laws.